Records you can defend.
Everchart isolates each clinic's data in the database itself, limits actions by role (admin, provider, staff), records logins, chart views, signatures and registry work in an append-only audit log without clinical text, locks signed notes and certification decisions, and stores documents privately behind short-lived signed links. HIPAA compliance also depends on hosting agreements and clinic policies, which we review with each clinic before real patient data is entered.
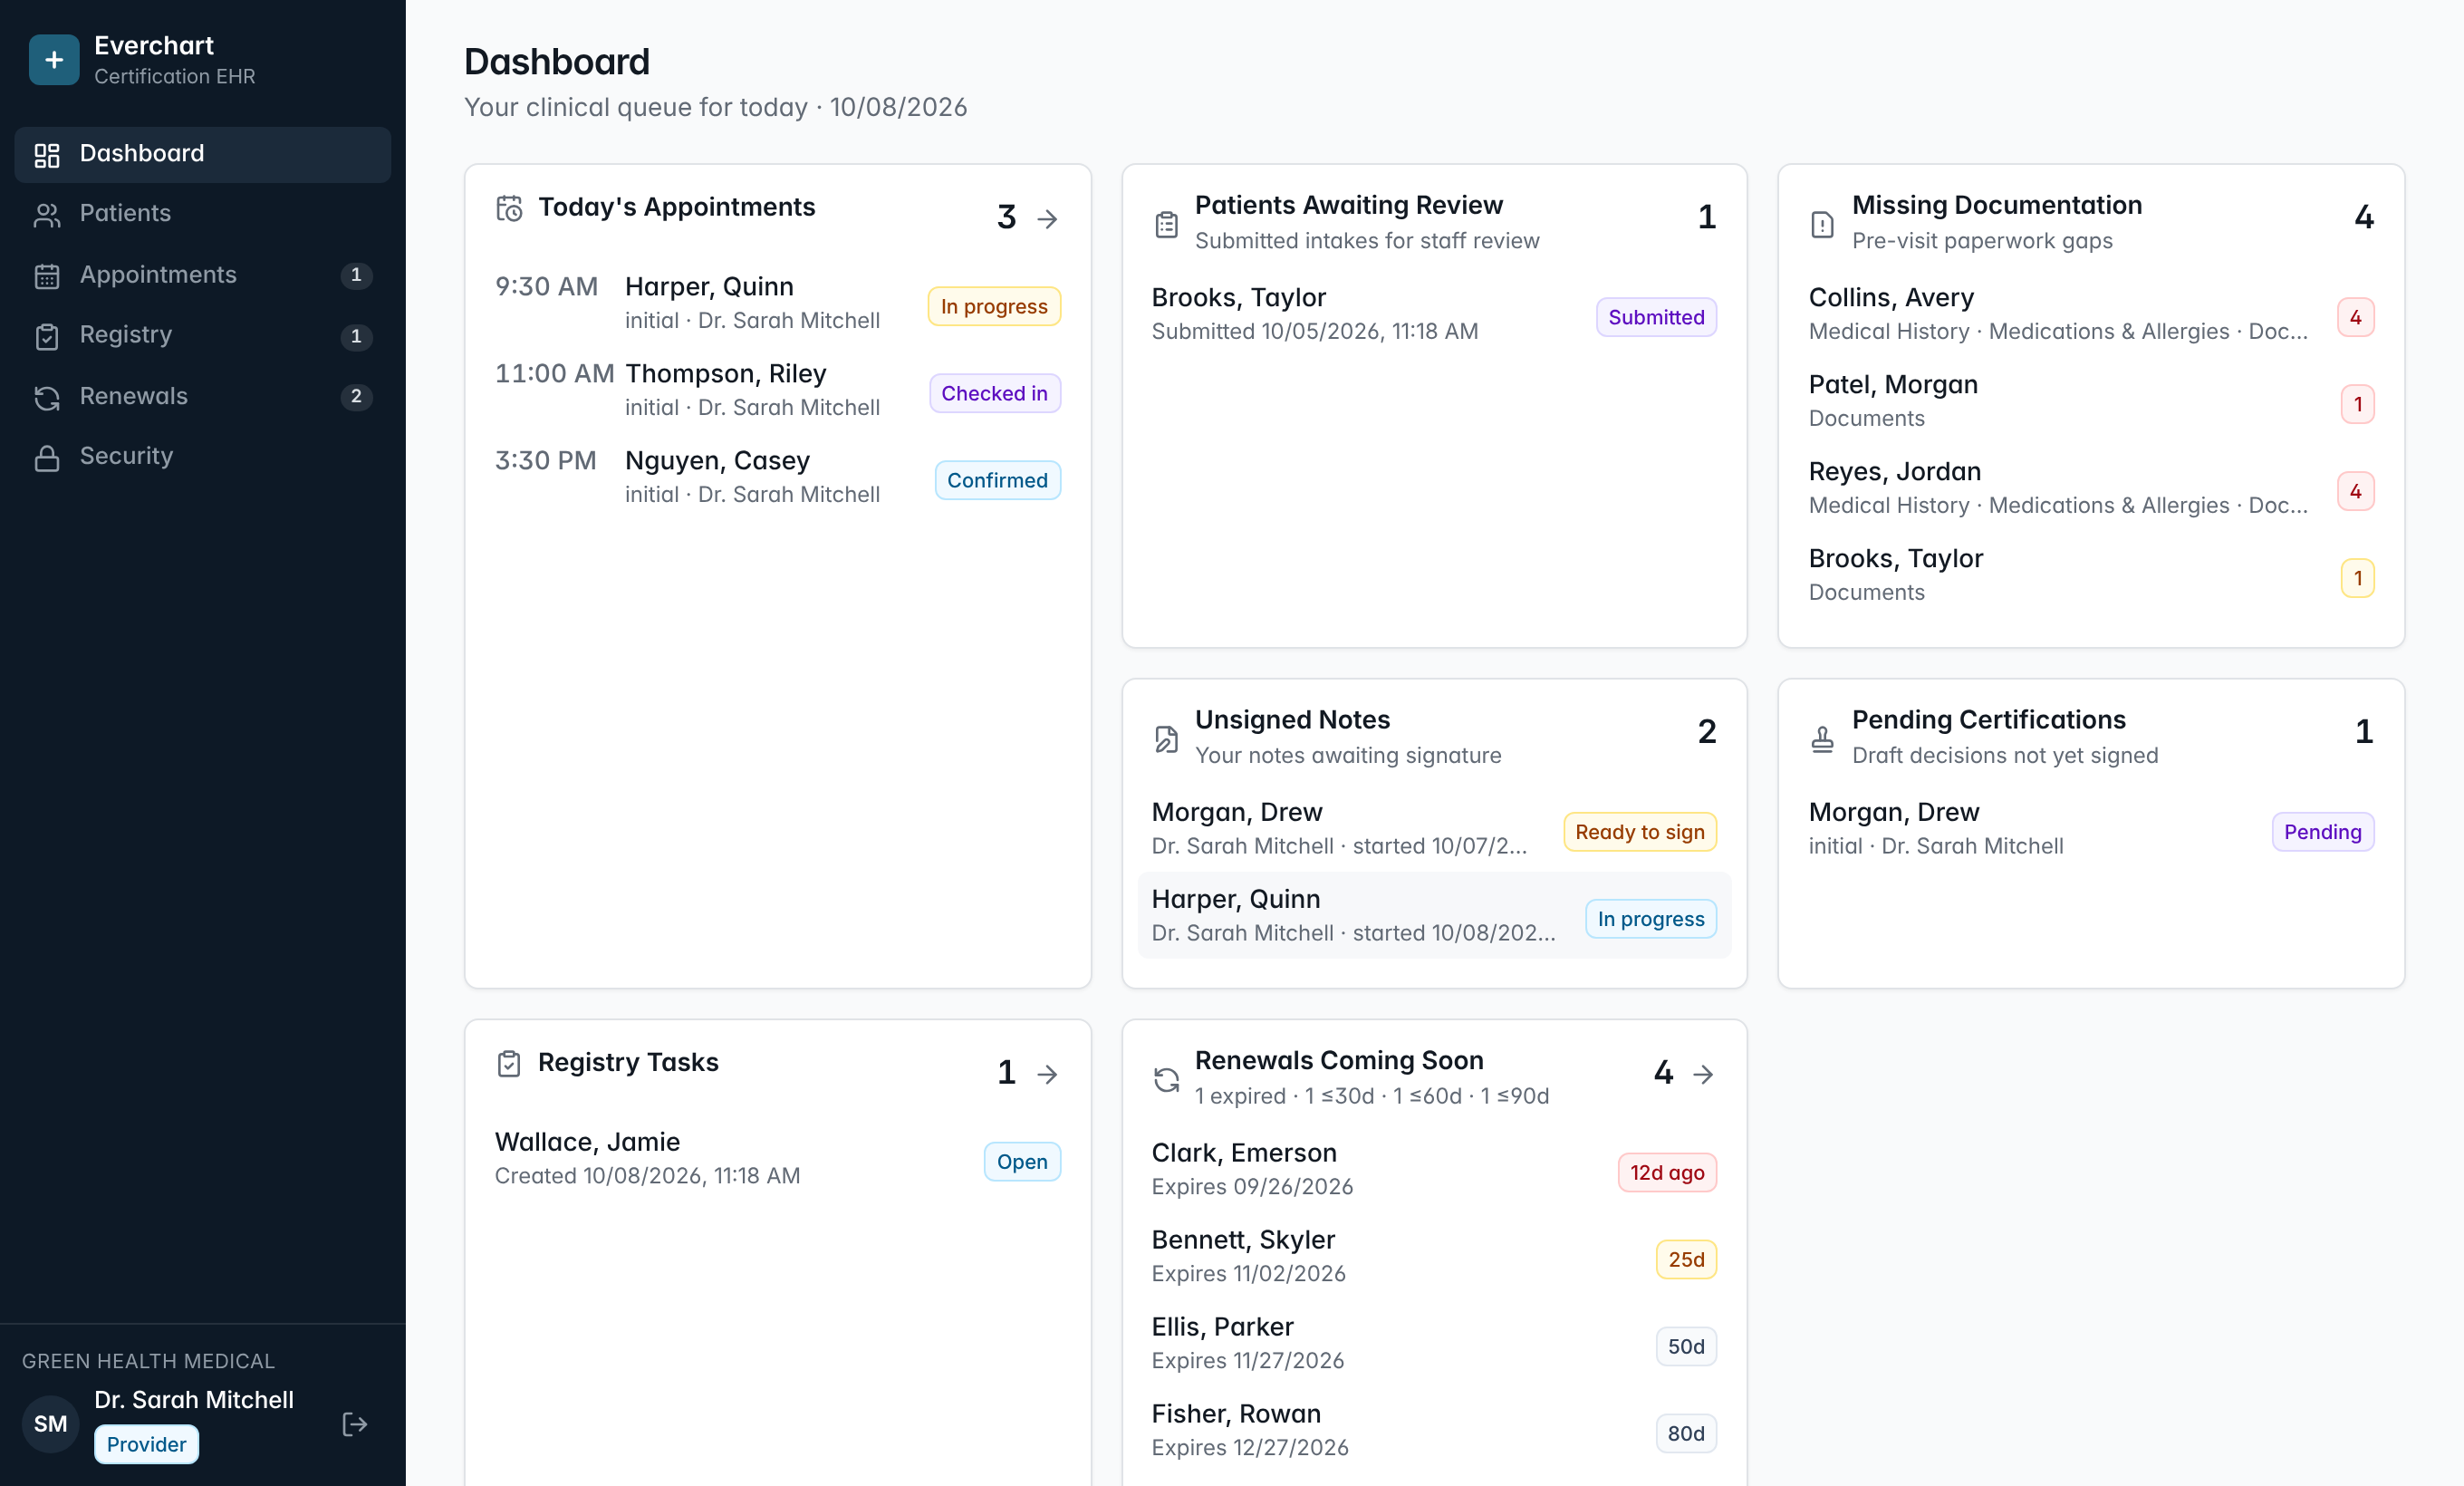
Clinic-level isolation
Every record carries its clinic and the database rejects cross-clinic references.
Role-based access
Admin, provider and staff roles with permissions enforced on the server.
Append-only audit log
Who did what and when, kept even from administrators' edits, and free of clinical text.
Private documents
File types are verified from their contents, stored privately and opened through expiring links.
How it works
- 1Staff and patients authenticate separately.
- 2Every request is scoped to the signed-in user's clinic and role.
- 3Sensitive actions are written to the audit log.
- 4Signed clinical records are frozen by database rules.
Common questions
Is it HIPAA compliant?
The software includes the safeguards HIPAA expects, but compliance depends on the full setup: signed BAAs with hosting vendors, a risk assessment and your clinic's policies. We walk through a BAA-backed production setup with you before any real patient data goes in.
Who can see the audit log?
Clinic administrators. Entries cannot be edited or deleted.
More features
See it running with your clinic's workflow.
A 30-minute live walkthrough using your state's process. No slides.